

Valid 300-410 Practice Test Dumps with 100% Passing Guarantee [Sep-2026]
300-410 PDF Dumps Are Helpful To produce Your Dreams Correct QA's
NEW QUESTION # 393
Which IPv6 feature enables a device to reject traffic when it is originated from an address that is
not stored in the device binding table?
- A. IPv6 Snooping
- B. IPv6 Source Guard
- C. IPv6 DAD Proxy
- D. IPv6 RA Guard
Answer: B
Explanation:
https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/ipv6_fhsec/configuration/xe-3s/ip6f-xe-3s-
book/ip6-src-guard.html
NEW QUESTION # 394
Refer to the exhibit. The administrator is trying to overwrite an existing file on the TFTP server
that was previously uploaded by another router. However, the attempt to update the file fails.
Which action resolves this issue?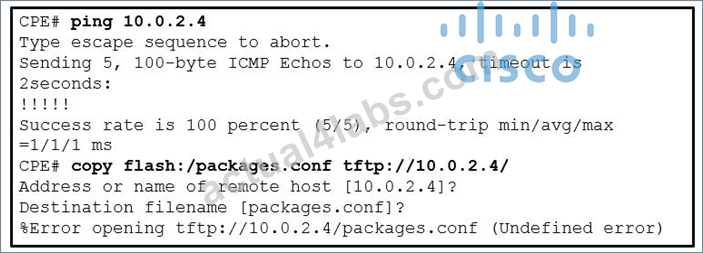
- A. Make the packages.conf file executable by all on the TFTP server
- B. Make the packages.conf file writable by all on the TFTP server
- C. Make sure to run the TFTP service on the TFTP server
- D. Make the TFTP folder writable by all on the TFTP server
Answer: B
Explanation:
During upload operations, if you are overwriting an existing file (including an empty file, if you had
to create one) on the server, ensure that the permissions on the file are set correctly. Permissions
on the file should be world-write.
NEW QUESTION # 395
Refer to the exhibit.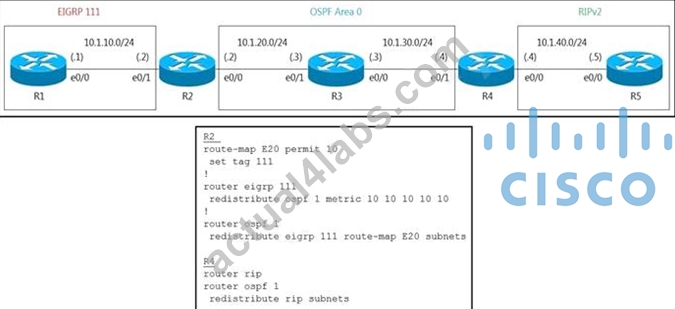
R5 should not receive any routes originated in the EIGRP domain. Which set of configuration changes removes the EIGRP routes from the R5 routing table to fix the issue?
- A. R2
route-map E20 deny 20
R4
route-map O2R deny 10
match tag 111
!
router rip
redistribute ospf 1 route-map O2R metric 1 - B. R4
route-map O2R permit 10
match tag 111
route-map O2R deny 20
!
router rip
redistribute ospf 1 route-map O2R metric 1 - C. R4
route-map O2R deny 10
match tag 111
!
router rip
redistribute ospf 1 route-map O2R metric 1 - D. R4
route-map O2R deny 10
match tag 111
route-map O2R permit 20
!
router rip
redistribute ospf 1 route-map O2R metric 1
Answer: D
Explanation:
In this question, routes from EIGRP domain are redistributed into OSPF (with tag 111) then RIPv2 but without any filtering so R5 learns all routes from both EIGRP and OSPF domain. If we only want R5 to learn routes from OSPF domain then we must filter out routes with tag 111 and permit other routes.
The line "route-map O2R permit 20" is important to allow other routes because of the implicit deny all at the end of each route-map.
NEW QUESTION # 396
When provisioning a device in Cisco Catalyst Center (formerly DNA Center), the engineer sees
the error message "Cannot select the device. Not compatible with template.". What is the reason
for the error?
- A. The software version of the template is different from the software version of the device
- B. The tag that was used to filter the templates does not match the device tag.
- C. The changes to the template were not committed
- D. The template has an incorrect configuration.
Answer: B
Explanation:
If you use tags to filter the templates, you must apply the same tags to the device to which you
want to apply the templates. Otherwise, you get the following error during provisioning: "Cannot
select the device. Not compatible with template."
Reference: https://www.cisco.com/c/en/us/td/docs/cloud-systems-management/network-
automation-and-management/dna-center/1-2-
10/user_guide/b_cisco_dna_center_ug_1_2_10/b_dnac_ug_1_2_10_chapter_0111.html
NEW QUESTION # 397
Refer to the exhibit.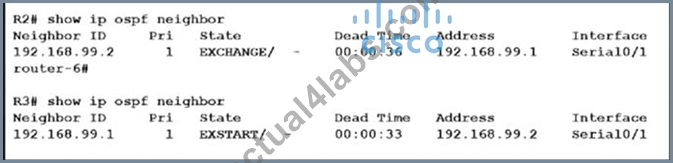
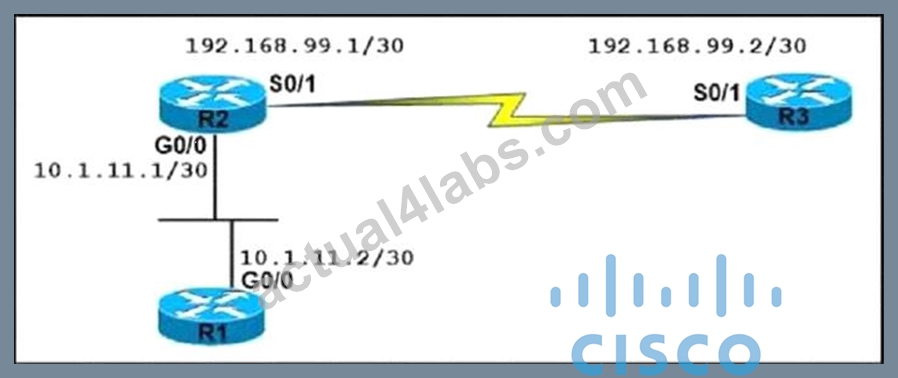
An OSPF neighbor relationship between R2 and R3 is showing stuck in EXCHANGE/EXSTART state. The neighbor is established between R1 and R2. The network engineer can ping from R2 to R3 and vice versa, but the neighbor is still down. Which action resolves the issue?
- A. Restore the Layer 2/Layer 3 conectivity issue in the ISP network.
- B. Enable OSPF on the interface, which is required.
- C. Match MTU on both router interfaces or ignore MTU.
- D. Administrative "shut then no shut" both router interfaces.
Answer: C
Explanation:
After two OSPF neighboring routers establish bi-directional communication and complete DR/BDR election (on multi-access networks), the routers transition to the exstart state. In this state, the neighboring routers establish a master/slave relationship and determine the initial database descriptor (DBD) sequence number to use while exchanging DBD packets.
Neighbors Stuck in Exstart/Exchange State
The problem occurs most frequently when attempting to run OSPF between a Cisco router and another vendor's router. The problem occurs when the maximum transmission unit (MTU) settings for neighboring router interfaces don't match. If the router with the higher MTU sends a packet larger that the MTU set on the neighboring router, the neighboring router ignores the packet.
NEW QUESTION # 398
Refer to the exhibit.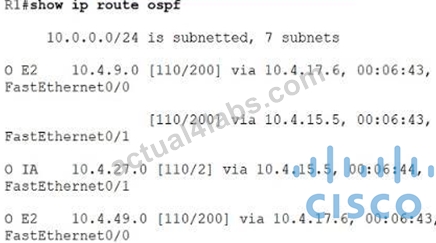
An engineer configures two ASBRs 10 4 17.6 and 10 4 15 5 in an OSPF network to redistribute routes from EIGRP However, both ASBRs show the EIGRP routes as equal costs even though the next-hop router 10 4 17
6 is closer to R1 How should the network traffic to the EIGRP prefixes be sent via 10 4.17.6?
- A. The ASBR 10 4 17 6 should assign a tag to match and assign a lower metnc on R1
- B. The redistributed prefixes should be advertised as Type 1
- C. The admitstrative distance should be raised to 120 from the ASBR 104 15.5.
- D. The administrative distance should be raised to 120 from the ASBR 104 17 6
- E. The redistributed prefixes should be advertised as Type 1.
- F. The ASBR 10 4 17 6 should assign a tag to match and assign a tower metnc on R1
- G. The administrative distance should be raised to 120 from the ASBR 104.17.6
- H. The administrative distance should be raised to 120 from the ASBR 10.4.15 5.
Answer: B
NEW QUESTION # 399
Refer to the exhibit.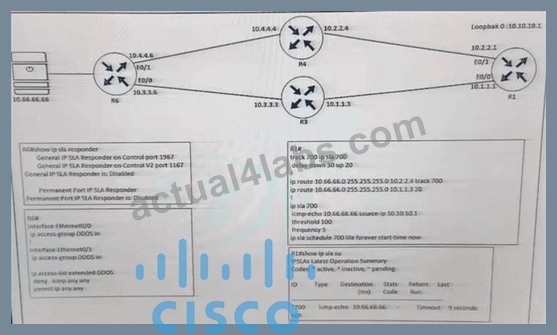
R1 is configured with IP SLA to check the availability of the server behind R6 but it kept failing. Which configuration resolves the issue?
- A. R6(config)# ip sla responder udp-echo ip address 10.10.10.1 port 5000
- B. R6(config)# ip access-list extended DDOSR6(confg ext-nac)# 5 permit icmp host 10.10.10.1 host
10.66.66.66 - C. R6(config)# ip sla responder
- D. R6(config)# ip access-list extended DDOSR6(config ext-nac)# 5 permit icmp host 10.66 66.66 host
10.10.10.1
Answer: B
Explanation:
In this IP SLA tracking, we don't need a IP SLA Responder so the command "ip sla responder" on R6 is not necessary.
We also notice that the ACL is blocking ICMP packets on both interfaces E0/0 & E0/1 of R6 so we need to allow ICMP from source 10.10.10.1 to destination 10.66.66.66.
NEW QUESTION # 400
Refer to the exhibit.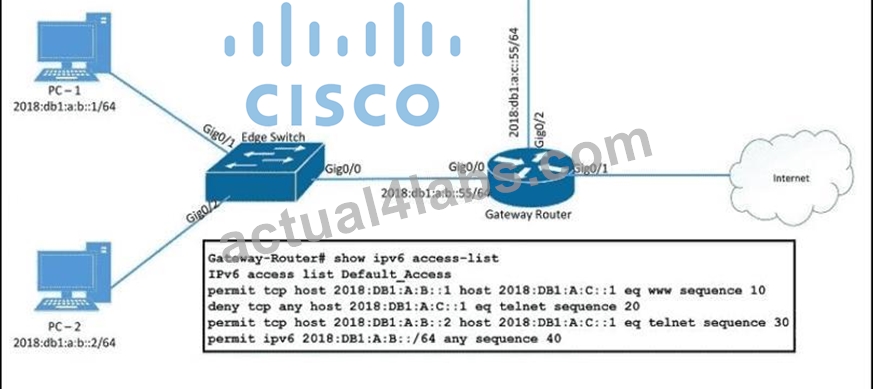
PC-2 failed to establish a Telnet connection to the terminal server. Which configuration resolves the issue?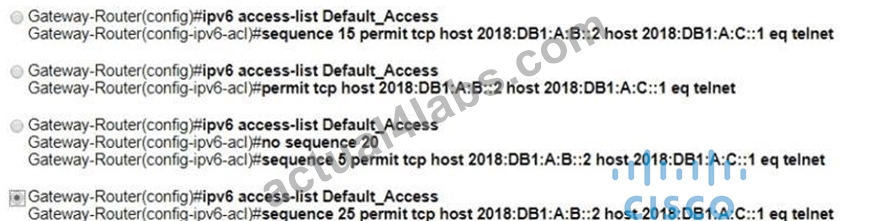
- A. Option D
- B. Option C
- C. Option A
- D. Option B
Answer: C
Explanation:
In fact in this question both answer A and answer C are correct but we believe answer A is the better choice as it only allows PC-2 to telnet to terminal server. All other hosts are refused to telnet to terminal server via sequence 20.
NEW QUESTION # 401
Refer to the exhibit. Which command must be configured to make VRF CCNP work?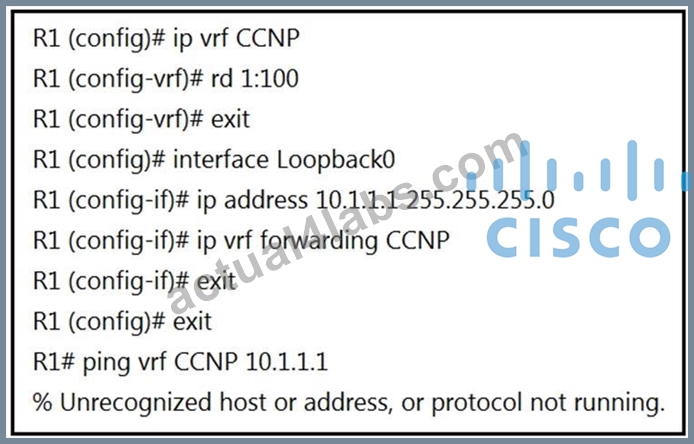
- A. interface Loopback0
ip address 10.1.1.1 255.255.255.0
vrf forwarding CCNP - B. interface Loopback0
ip address 10.1.1.1 255.255.255.0 - C. interface Loopback0
vrf forwarding CCNP - D. interface Loopback0
ip address 10.1.1.1 255.255.255.0
ip vrf forwarding CCNP
Answer: B
NEW QUESTION # 402
Drag and drop the operations from the left onto the locations where the operations are performed on the right.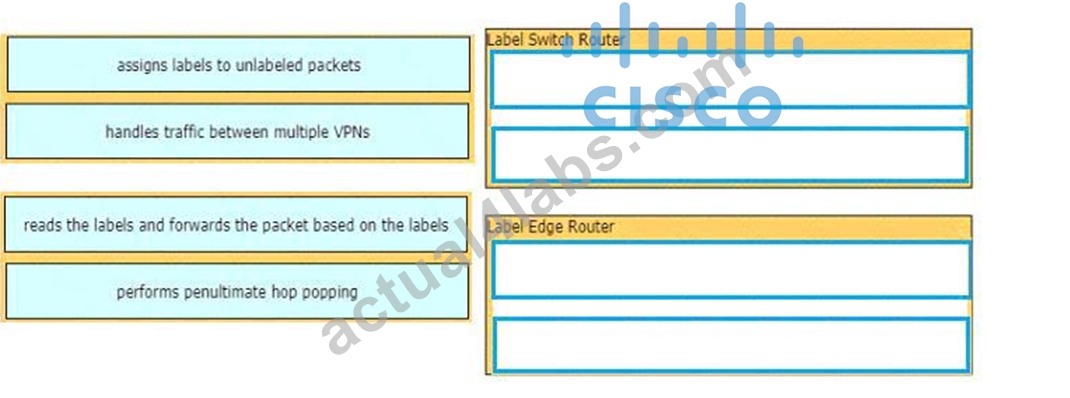
Answer:
Explanation: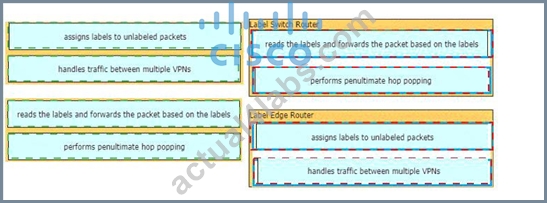
Explanation
Label Switch Router 1. Reads labels and forwards the packet based on the based on the label.
2. Performs PHP
Label Edge Router: 1 Assigns labels and unlabeled packets.
2. Handles traffic between multiple VPNs
NEW QUESTION # 403
Refer to the exhibit.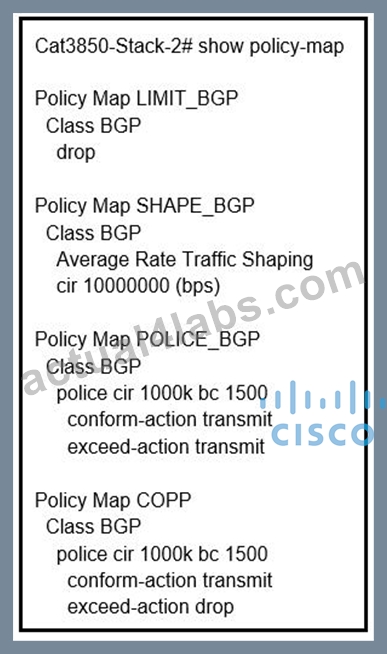
Which control plane policy limits BGP traffic that is destined to the CPU to 1 Mbps and ignores BGP traffic that is sent at higher rate?
- A. policy-map COPP
- B. policy-map POLICE_BGP
- C. policy-map LIMIT_BGP
- D. policy-map SHAPE_BGP
Answer: A
NEW QUESTION # 404 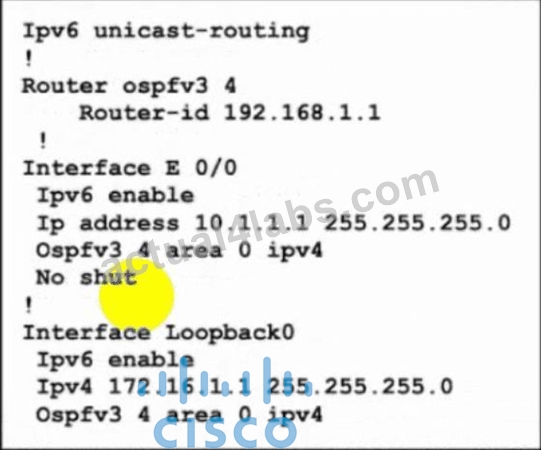
Refer to the exhibit. The network administrator configured the branch router for IPv6 on the E 0/0 interface The neighboring router is fully configured to meet requirements, but the neighbor relationship is not coming up. Which action fixes the problem on the branch router to bring the IPv6 neighbors up?
- A. Enable the IPv4 address family under the E 0/0 interface by using the address-family Ipv4 unicast command
- B. Disable OSPF for IPv4 using the no ospfv3 4 area 0 ipv4 command under the E 0/0 interface.
- C. Enable the IPv4 address family under the router ospfv3 4 process by using the address-family ipv4 unicast command
- D. Disable IPv6 on the E 0/0 interface using the no ipv6 enable command
Answer: C
Explanation:
Once again, Cisco changed the IOS configuration commands required for OSPFv3 configuration. The new OSPFv3 configuration uses the "ospfv3" keyword instead ofthe earlier "ipv6 router ospf" routing process command and "ipv6 ospf" interface commands.
The Open Shortest Path First version 3 (OSPFv3) address families feature enables both IPv4 and IPv6 unicast traffic to be supported. With this feature, users may havetwo processes per interface, but only one process per address family (AF).
NEW QUESTION # 405
Refer to the exhibit. A network engineer is troubleshooting a failed link between R2 and R3. No
traffic loss is reported from router R5 to HQ. Which command fixes the separated backbone?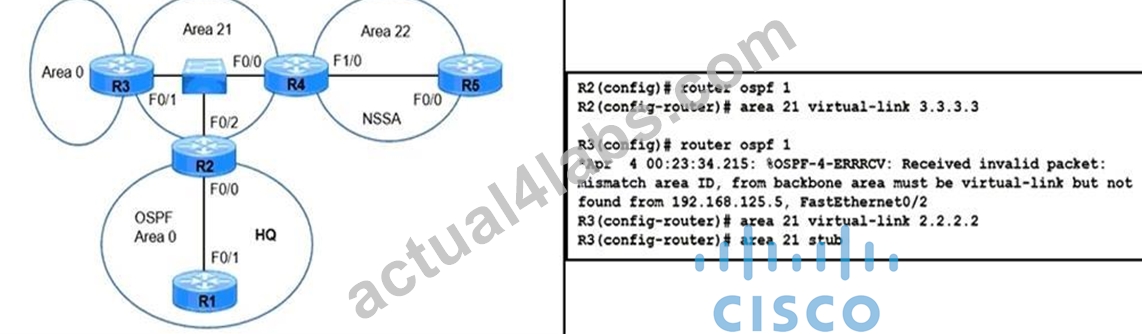
- A. R3(config-router)#area 21 virtual-link 192.168.125.5
- B. R3(config-router)#no area 21 stub
- C. R2(config-router)#no area 21 stub
- D. R2(config-router)#area 21 virtual-link 192.168.125.5
Answer: D
NEW QUESTION # 406
Refer to the exhibit. Packets arriving from source 209.165.200.215 must be sent with the precedence bit set to 1, and packets arriving from source 209.165.200.216 must be sent with the precedence bit set to 5. Which action resolves the issue?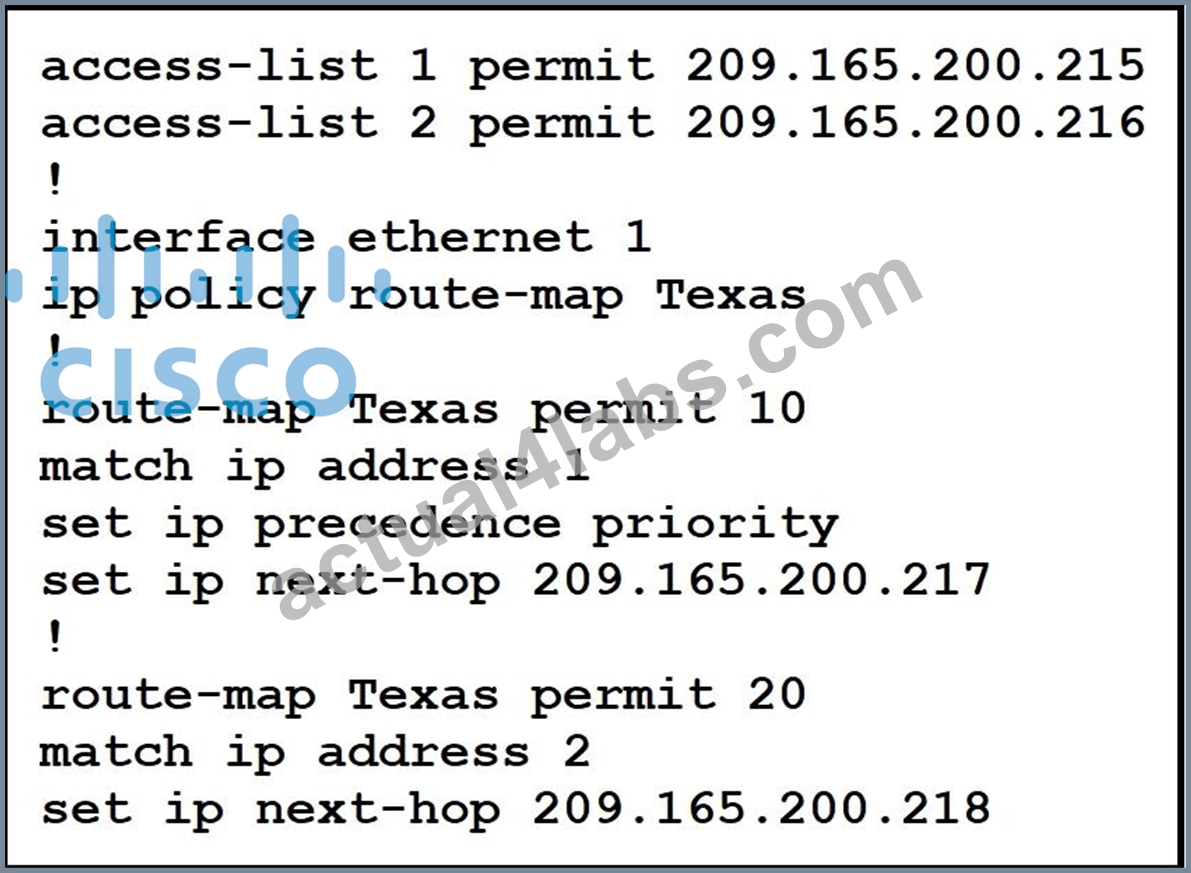
- A. set ip precedence immediate in route-map Texas permit 10
- B. set ip precedence critical in route-map Texas permit 10
- C. set ip precedence priority in route-map Texas permit 20
- D. set ip precedence critical in route-map Texas permit 20
Answer: D
Explanation:
You can change the precedence setting, using either a number or name (the names came from RFC 791). You can enable other features that use the values in the set ip precedence route map configuration command to determine precedence. The table below lists the possible numbers and their corresponding name, from lowest to highest precedence.
NEW QUESTION # 407 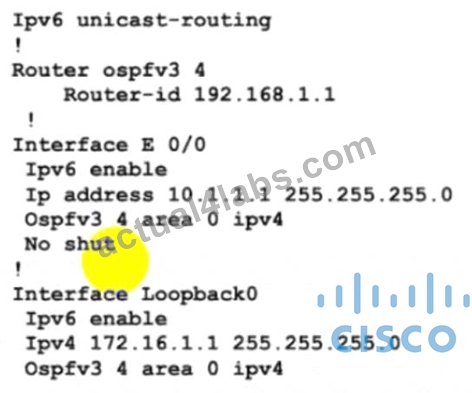
Refer to the exhibit. The network administrator configured the branch router for IPv6 on the E 0/0 interface The neighboring router is fully configured to meet requirements, but the neighbor relationship is not coming up. Which action fixes the problem on the branch router to bring the IPv6 neighbors up?
- A. Enable the IPv4 address family under the E 0/0 interface by using the address-family Ipv4 unicast command
- B. Disable OSPF for IPv4 using the no ospfv3 4 area 0 ipv4 command under the E 0/0 interface.
- C. Enable the IPv4 address family under the router ospfv3 4 process by using the address-family ipv4 unicast command
- D. Disable IPv6 on the E 0/0 interface using the no ipv6 enable command
Answer: C
Explanation:
Once again, Cisco changed the IOS configuration commands required for OSPFv3 configuration. The new OSPFv3 configuration uses the "ospfv3" keyword instead ofthe earlier "ipv6 router ospf" routing process command and "ipv6 ospf" interface commands.
The Open Shortest Path First version 3 (OSPFv3) address families feature enables both IPv4 and IPv6 unicast traffic to be supported. With this feature, users may havetwo processes per interface, but only one process per address family (AF).
NEW QUESTION # 408 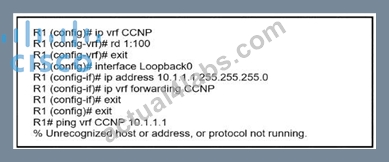
Refer to the exhibit Which command must be configured to make VRF CCNP work?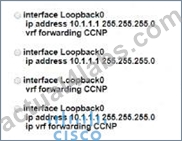
- A. Option D
- B. Option B
- C. Option C
- D. Option A
Answer: B
NEW QUESTION # 409
Refer to the exhibit. The administrator can see the traps for the failed login attempts, but cannot
see the traps of successful login attempts. What command is needed to resolve the issue?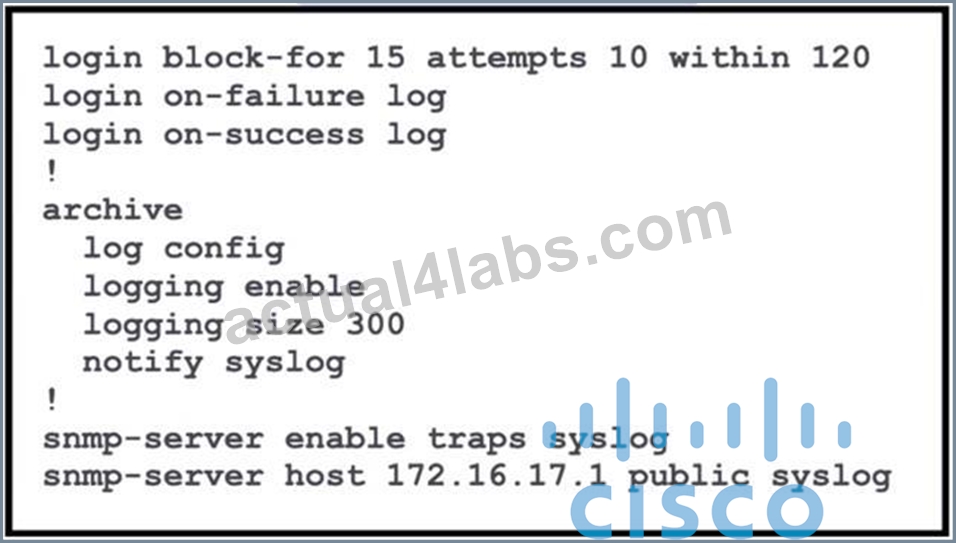
- A. Configure logging history 5
- B. Configure logging history 3
- C. Configure logging history 2
- D. Configure logging history 4
Answer: A
Explanation:
By default, the maximum severity sent as a syslog trap is warning. That is why you see syslog
traps for login failures. Since a login success is severity 5 (notifications), those syslog messages
will not be converted to traps. To fix this, configure: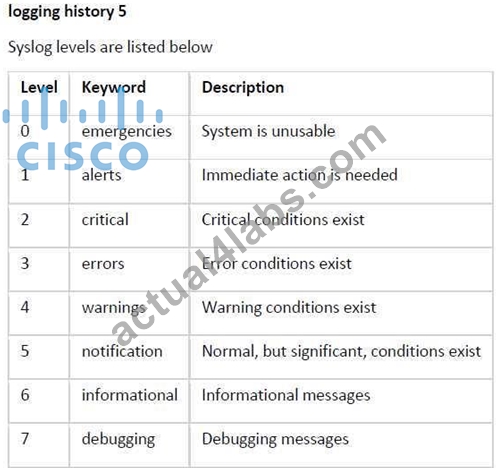
Note:
The syntax of login block is:
login block-for seconds attempts tries within seconds
NEW QUESTION # 410
Refer to the exhibit.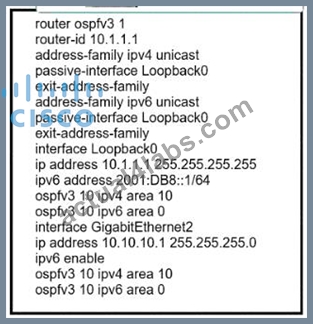
An engineer noticed that the router log messages do not have any information about when the event occurred. Which action should the engineer take when enabling service time stamps to improve the logging functionality at a granular level?
- A. Replace OSPF process 10 on the interfaces with OSPF process 1 and configure an additional router IO with IPv6 address
- B. Replace OSPF process 10 on the interfaces with OSPF process 1 for the IPv4 address and remove process 10 from the global configuration
- C. Replace OSPF process 10 on the interfaces with OSPF process 1 for the IPv6 address and remove process 10 from the global configuration
- D. Replace OSPF process 10 on the interfaces with OSPF process 1. and remove process 10 from the global configuration
Answer: B
NEW QUESTION # 411
Which two components are needed for a service provider to utilize the LVPN MPLS application? (Choose two.)
- A. The PE routers must be configured for MP-eBGP to connect to CEs
- B. The P and PE routers must be configured with LDP or RSVP
- C. The PE routers must be configured for MP-iBGP with other PE routers
- D. The P routers must be configured with RSVP.
- E. The P routers must be configured for MP-iBGP toward the PE routers
Answer: A,E
NEW QUESTION # 412
An engineer must override the normal routing behavior of a router for Telnet traffic that is
destined to 10.10.10.10 from 10.10.1.0/24 via a next hop of 10.4.4.4 which is directly connected
to the router that is connected to the 10.1.1.0/24 subnet.
Which configuration reroutes traffic according to this requirement?
- A. access-list 100 permit tcp 10.1.1.0 0.0.0.255 host 10.100.100.100 eq http
!
route-map POLICY permit 10
match ip address 100
set ip next-hop 10.2.2.2 - B. access-list 100 permit tcp 10.1.1.0 0.0.0.255 host 10.100.100.100 eq http
!
route-map POLICY deny 10
match ip address 100
set ip next-hop recursive 10.2.2.2
route-map POLICY permit 20 - C. access-list 100 permit tcp 10.1.1.0 0.0.0.255 host 10.100.100.100 eq http
!
route-map POLICY permit 10
match ip address 100
set ip next-hop 10.2.2.2
route-map POLICY permit 20 - D. access-list 100 permit tcp 10.1.1.0 0.0.0.255 host 10.100.100.100 eq http
!
route-map POLICY permit 10
match ip address 100
set ip next-hop recursive 10.2.2.2
Answer: D
NEW QUESTION # 413
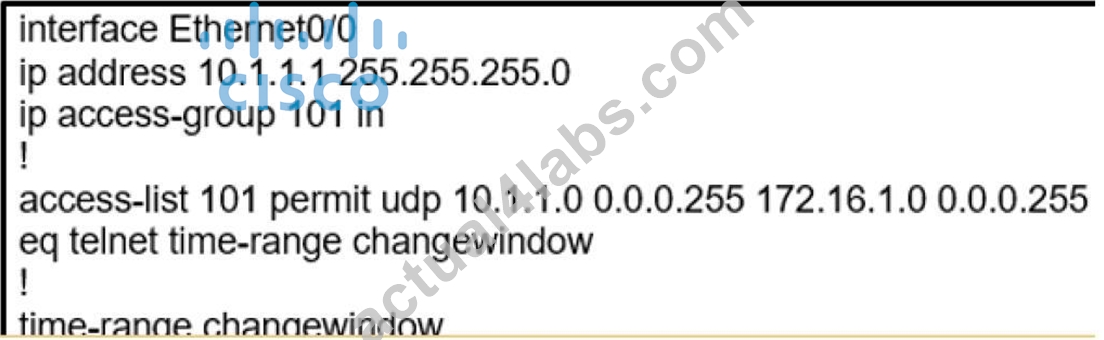
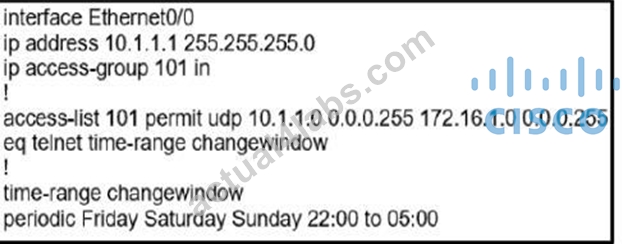
During the maintenance window an administrator accidentally deleted the Telnet-related configuration that permits a Telnet connection from the inside network (Eth0/0) to the outside of the networking between Friday - Sunday night hours only. Which configuration resolves the issue?
- A.
- B.
- C.
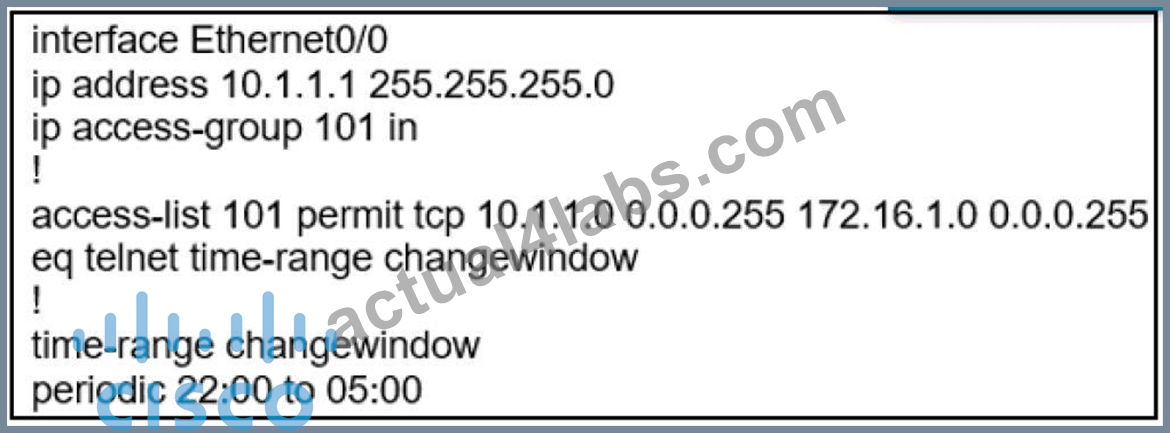
- D.
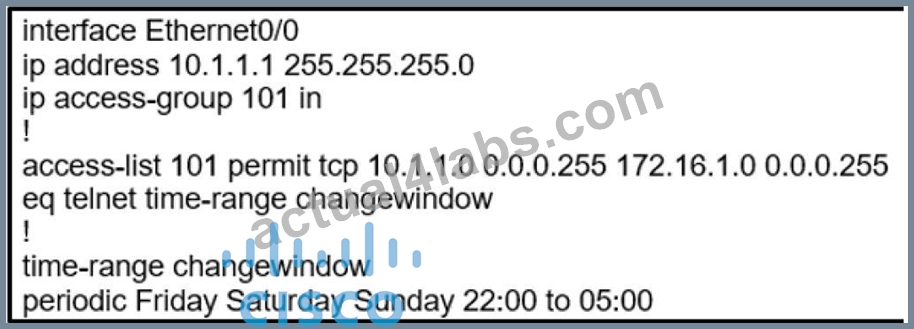
Answer: D
NEW QUESTION # 414
A customer reports that traffic is not passing on an EIGRP enabled multipoint interface on a router configured as below: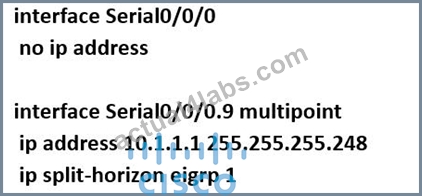
Which action resolves the issue?
- A. Enable split horizon
- B. Disable poison reverse
- C. Disable split horizon
- D. Enable poison reverse
Answer: C
Explanation:
On multipoint interfaces such as Frame Relay or DMVPN, split horizon prevents routes learned from one neighbor from being advertised to others on the same interface. Disabling split horizon allows the router to share routes between neighbors, restoring traffic flow.
NEW QUESTION # 415 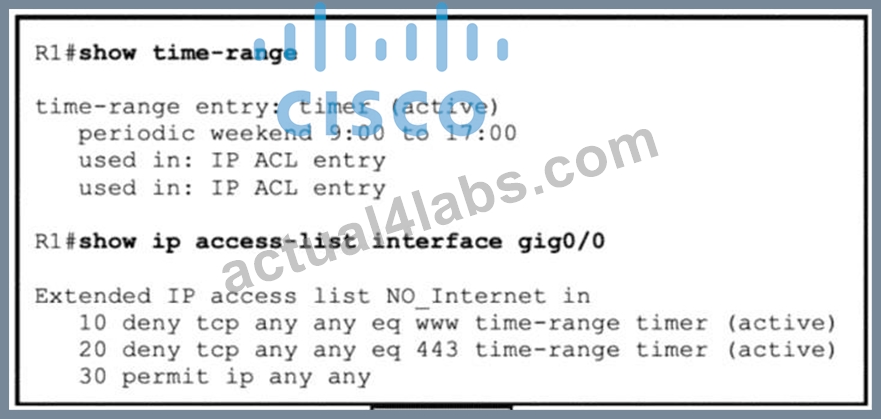
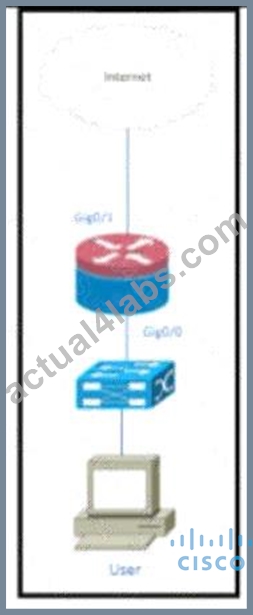
Refer to the exhibit. Users on a call center report that they cannot browse the internet on Saturdays during the afternoon. Which configuration resolves the issue?
- A.
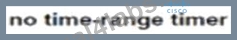
- B.
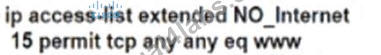
- C.
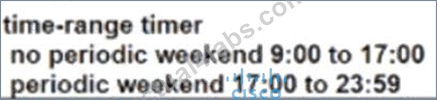
- D.
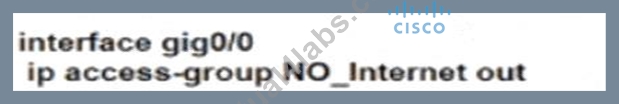
Answer: C
NEW QUESTION # 416
Refer to the exhibit.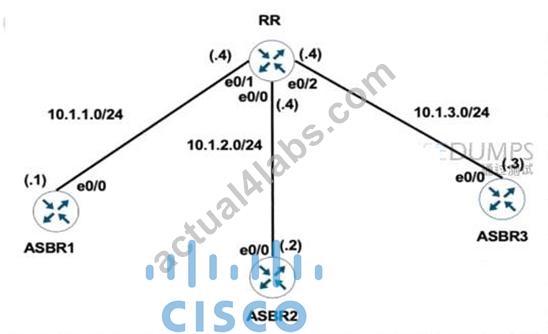
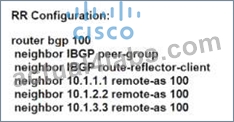
The network administrator configured the network to establish connectivity between all devices and notices that the ASBRs do not have routes for each other. Which set of configurations resolves this issue?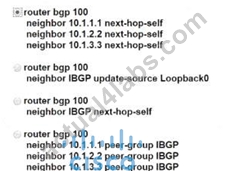
- A. Option D
- B. Option C
- C. Option B
- D. Option A
Answer: A
NEW QUESTION # 417
Exhibit.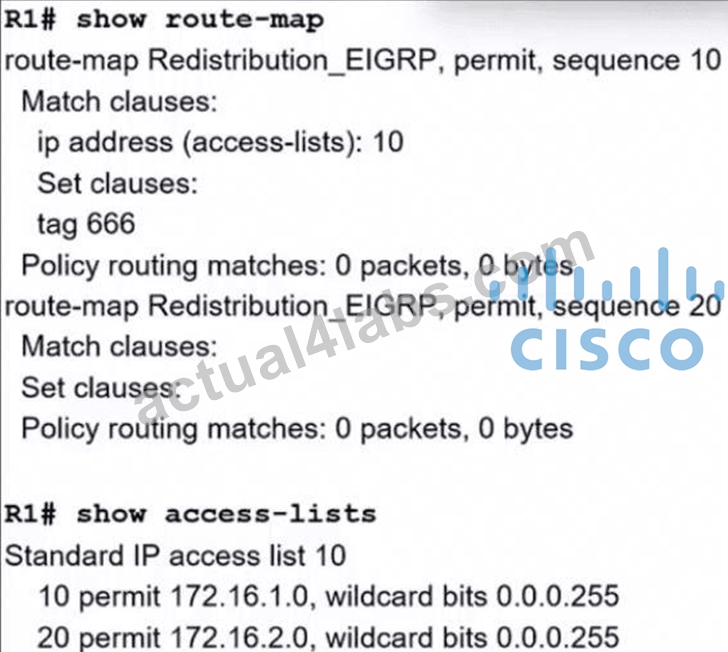
Refer to the exhibit. The router is redistil bating a prefix 172.16.10.0tt4 that should have been filtered. Which action resolves the issue?
- A. Remove route-map sequence 20.
- B. Permit the route in route-map sequence 20.
- C. Match the tag 666 for the route in the route map.
- D. Add the route in access-list 10.
Answer: A
NEW QUESTION # 418
......
Cover 300-410 Exam Questions Make Sure You 100% Pass: https://www.actual4labs.com/Cisco/300-410-actual-exam-dumps.html
New 300-410 exam Free Sample Questions to Practice: https://drive.google.com/open?id=1TefcknoXEQ367tCULRTgpRjYST3-3R3a