

Updated Dec 23, 2024 Test Engine to Practice Test for SC-200 Valid and Updated Dumps
Exam Questions for SC-200 Updated Versions With Test Engine
Microsoft SC-200 exam covers a wide range of security topics such as incident response, threat intelligence, security operations, and vulnerability management. SC-200 exam also assesses the candidate's ability to use security tools such as Azure Sentinel, Azure Security Center, and Microsoft Defender for Endpoint. Microsoft Security Operations Analyst certification validates the candidate's ability to apply security best practices and use Microsoft security technologies to protect an organization's network environment.
Microsoft SC-200 Exam, also known as the Microsoft Security Operations Analyst Exam, is a certification exam designed for professionals seeking to validate their skills and knowledge in security operations, incident response, and threat management. Microsoft Security Operations Analyst certification is ideal for those responsible for detecting, investigating, and responding to security incidents using a variety of tools, techniques, and procedures.
NEW QUESTION # 22
You need to use an Azure Sentinel analytics rule to search for specific criteria in Amazon Web Services (AWS) logs and to generate incidents.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.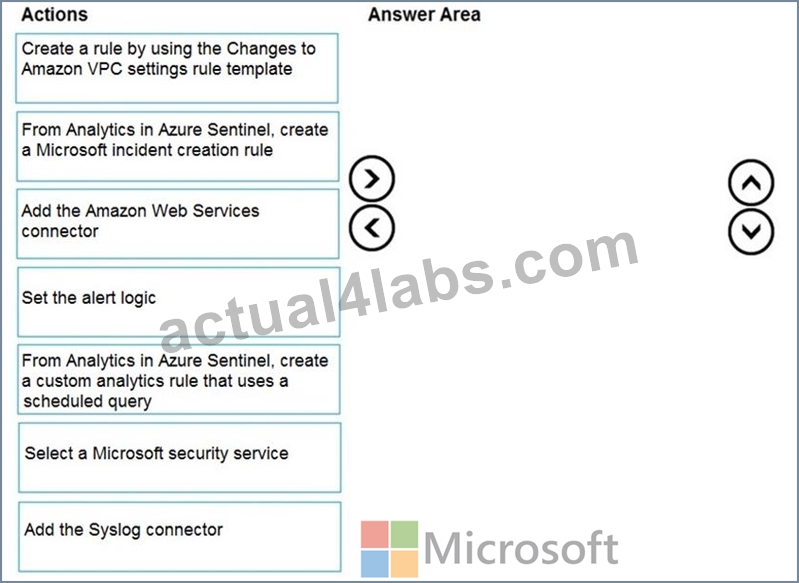
Answer:
Explanation: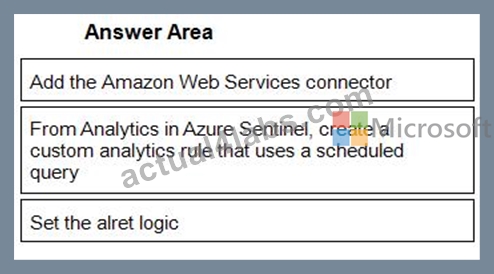
1 - Add the Amazon Web Services connector
2 - From Analytics in Azure Sentinel, create a custom analytics rule that uses a scheduled query
3 - Set the alret logic
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/detect-threats-custom
NEW QUESTION # 23
You need to implement Azure Defender to meet the Azure Defender requirements and the business requirements.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.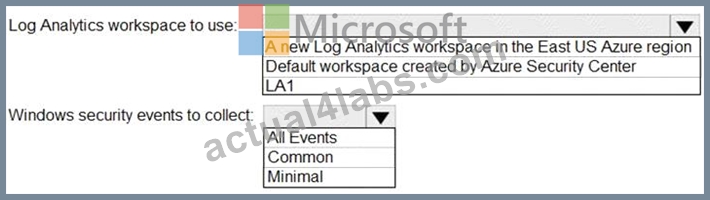
Answer:
Explanation: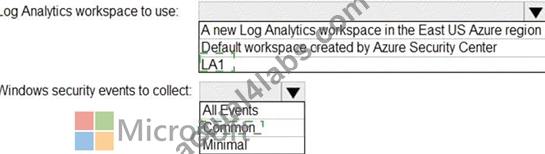
Explanation: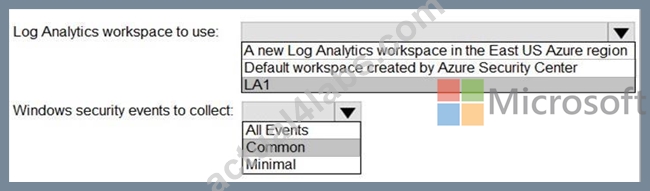
NEW QUESTION # 24
You manage the security posture of an Azure subscription that contains two virtual machines name vm1 and vm2.
The secure score in Azure Security Center is shown in the Security Center exhibit. (Click the Security Center tab.)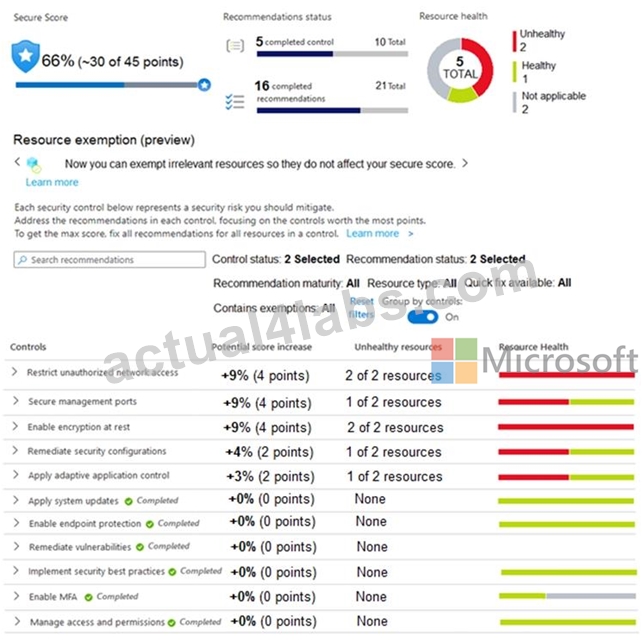
Azure Policy assignments are configured as shown in the Policies exhibit. (Click the Policies tab.)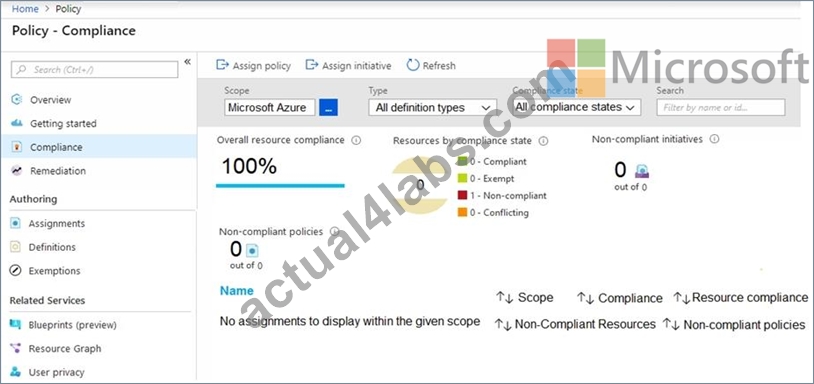
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.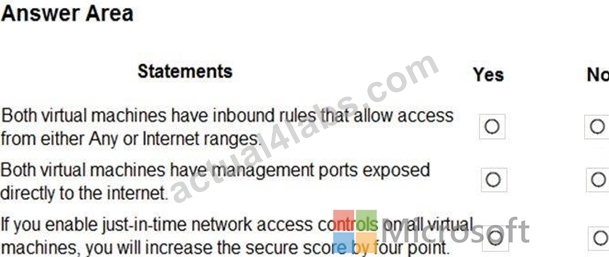
Answer:
Explanation: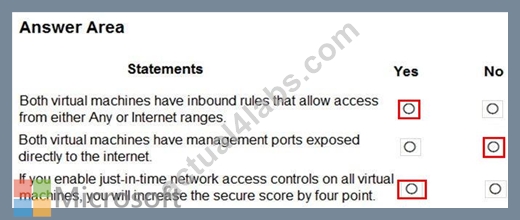
Reference:
https://techcommunity.microsoft.com/t5/azure-security-center/security-control-restrict-unauthorized-network-access/ba-p/1593833
https://techcommunity.microsoft.com/t5/azure-security-center/security-control-secure-management-ports/ba-p/1505770
NEW QUESTION # 25
You have a Microsoft Sentinel workspace named Workspaces
You need to exclude a built-in. source-specific Advanced Security Information Model (ASIM) parser from a built-in unified ASIM parser.
What should you create in Workspace1?
- A. a workbook
- B. an analytic rule
- C. a watchlist
- D. a hunting query
Answer: B
Explanation:
Explanation
To exclude a built-in, source-specific Advanced Security Information Model (ASIM) parser from a built-in unified ASIM parser, you should create an analytic rule in the Microsoft Sentinel workspace. An analytic rule allows you to customize the behavior of the unified ASIM parser and exclude specific source-specific parsers from being used. Reference: https://docs.microsoft.com/en-us/azure/sentinel/analytics-create-analytic-rule
NEW QUESTION # 26
You need to use an Azure Sentinel analytics rule to search for specific criteria in Amazon Web Services (AWS) logs and to generate incidents.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
a Microsoft 365 E5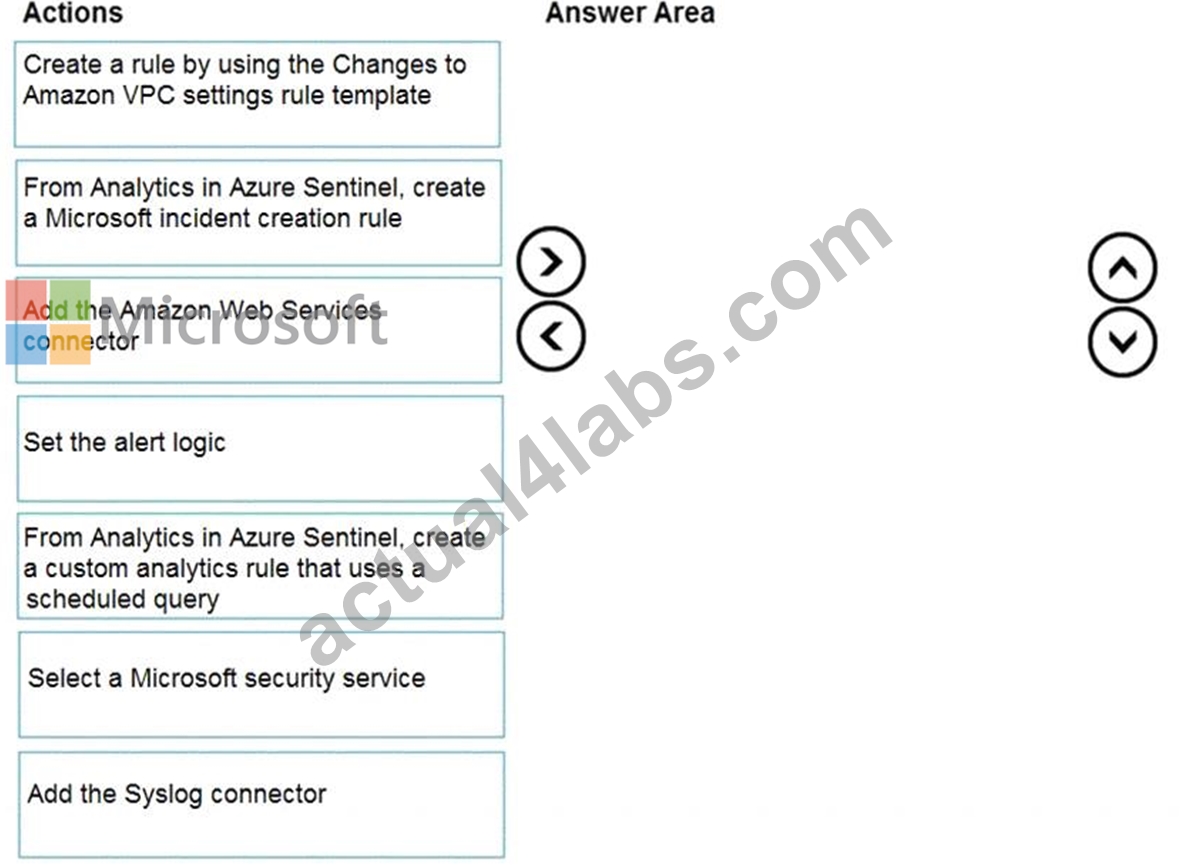
Answer:
Explanation: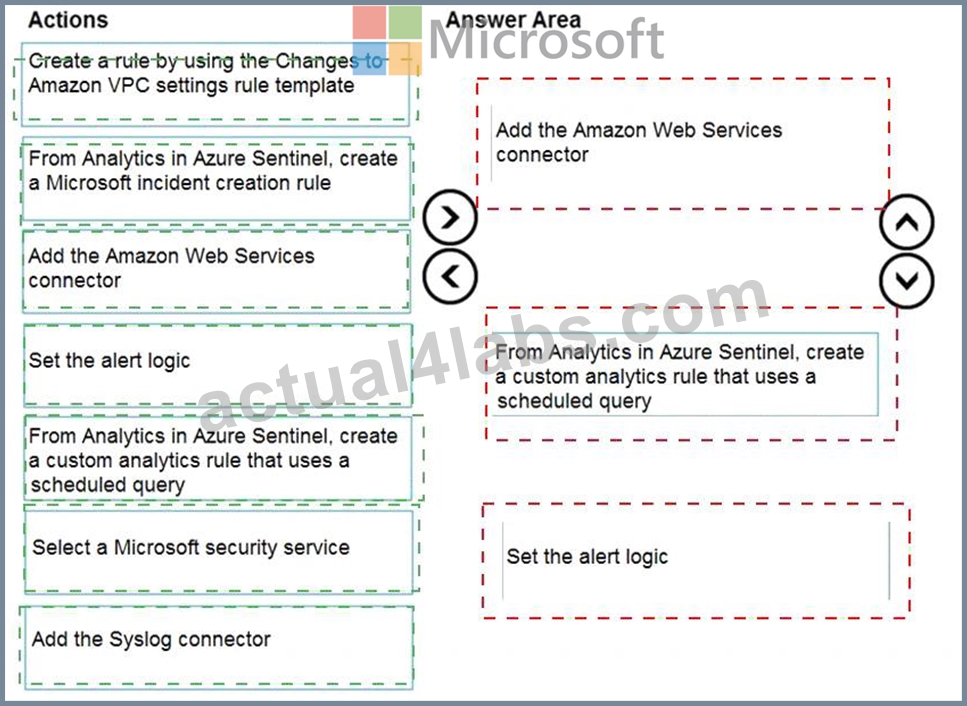
Explanation
Graphical user interface, text, application Description automatically generated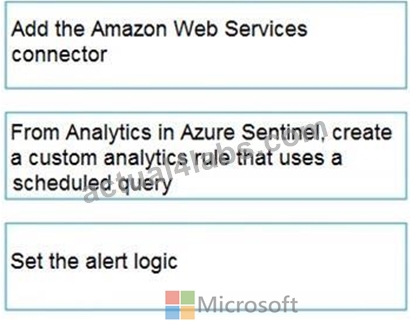
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/detect-threats-custom
NEW QUESTION # 27
You need to configure the Azure Sentinel integration to meet the Azure Sentinel requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.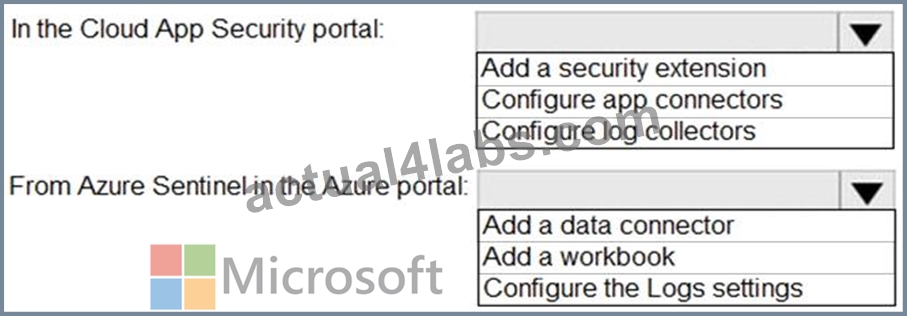
Answer:
Explanation: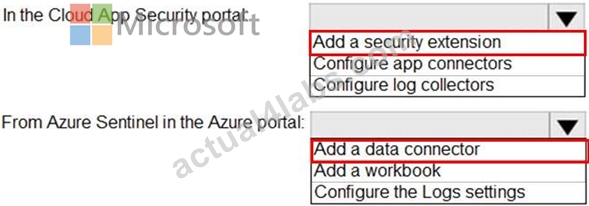
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/siem-sentinel
NEW QUESTION # 28
You have a Microsoft Sentinel workspace.
You have a query named Query1 as shown in the following exhibit.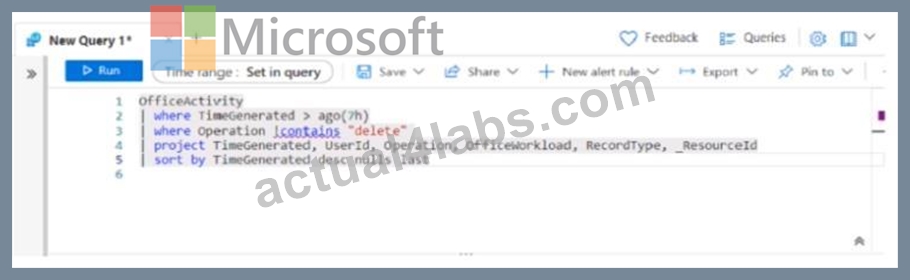
You plan to create a custom parser named Parser 1. You need to use Query1 in Parser1. What should you do first?
- A. In line 3, replace the 'contains operator with the !has operator.
- B. Remove line 2.
- C. Remove line 5.
- D. In line 4. remove the TimeGenerated predicate.
Answer: B
Explanation:
Explanation
This can be confirmed by referring to the official Microsoft documentation on creating custom log queries in Azure Sentinel, which states that the "has" operator should not be used in the query, and that it is unnecessary.
Reference: https://docs.microsoft.com/en-us/azure/sentinel/query-custom-logs
NEW QUESTION # 29
You have an existing Azure logic app that is used to block Azure Active Directory (Azure AD) users. The logic app is triggered manually.
You deploy Azure Sentinel.
You need to use the existing logic app as a playbook in Azure Sentinel. What should you do first?
- A. Add a data connector to Azure Sentinel.
- B. Modify the trigger in the logic app.
- C. Configure a custom Threat Intelligence connector in Azure Sentinel.
- D. And a new scheduled query rule.
Answer: B
Explanation:
https://docs.microsoft.com/en-us/azure/sentinel/playbook-triggers-actions
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-respond-threats-playbook
NEW QUESTION # 30
You have a Microsoft Sentinel workspace.
You need to create a KQL query that will identify successful sign-ins from multiple countries during the last three hours.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE Each correct selection is worth one point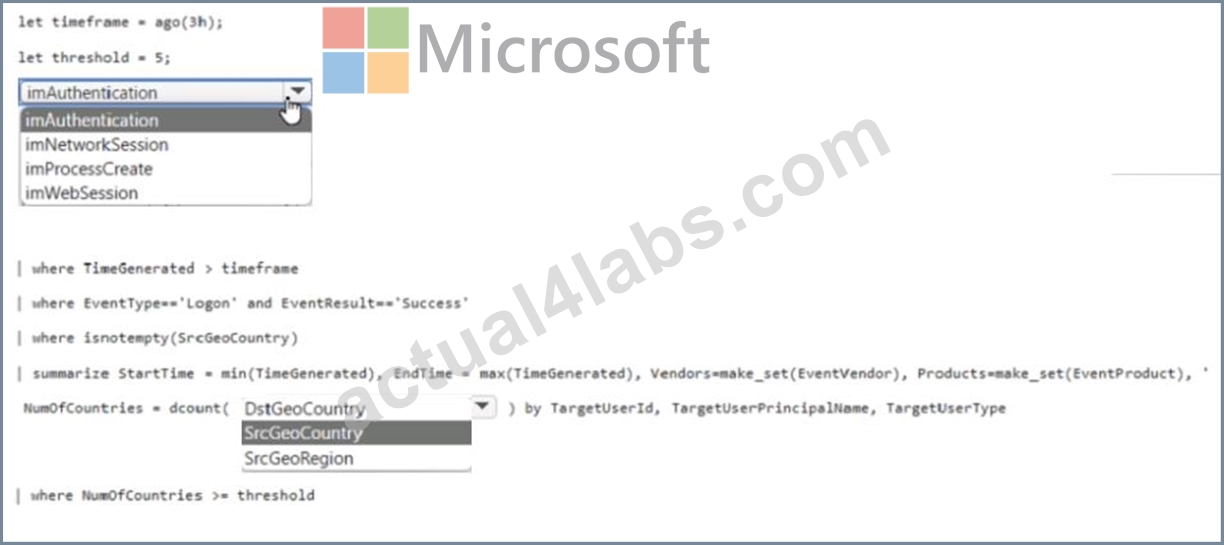
Answer:
Explanation: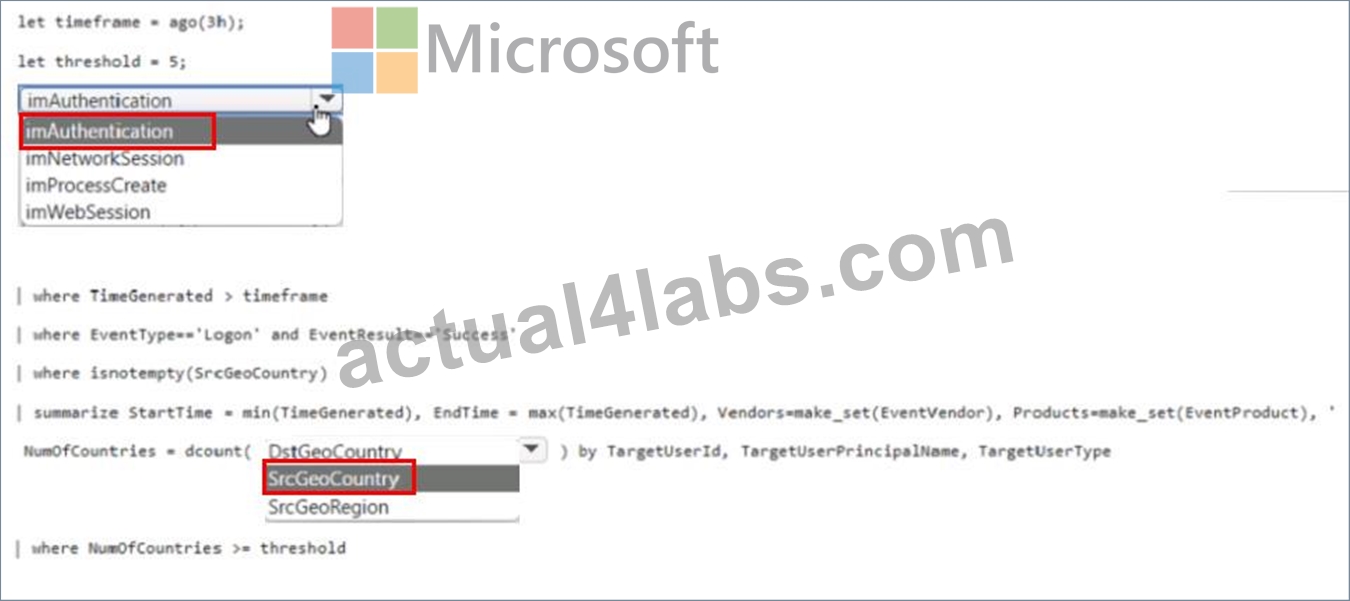
NEW QUESTION # 31
You need to implement Azure Defender to meet the Azure Defender requirements and the business requirements.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 32
You need to complete the query for failed sign-ins to meet the technical requirements.
Where can you find the column name to complete the where clause?
- A. Security alerts in Azure Security Center
- B. the query windows of the Log Analytics workspace
- C. Activity log in Azure
- D. Azure Advisor
Answer: B
NEW QUESTION # 33
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Microsoft Defender for Identity integration with Active Directory.
From the Microsoft Defender for identity portal, you need to configure several accounts for attackers to exploit.
Solution: You add the accounts to an Active Directory group and add the group as a Sensitive group.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/defender-for-identity/manage-sensitive-honeytoken-accounts
NEW QUESTION # 34
You need to create an advanced hunting query to investigate the executive team issue.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.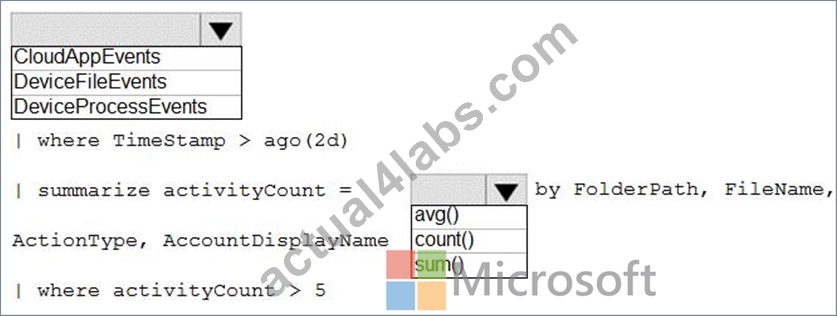
Answer:
Explanation: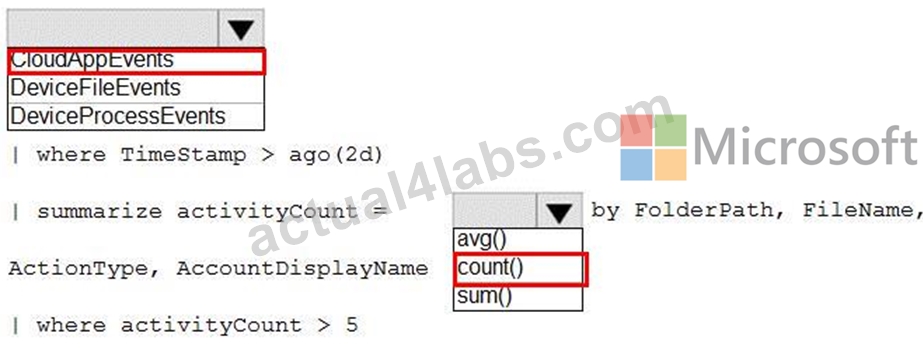
NEW QUESTION # 35
You have a Microsoft 365 subscription that uses Microsoft Purview.
Your company has a project named Project1.
You need to identify all the email messages that have the word Project1 in the subject line. The solution must search only the mailboxes of users that worked on Project1.
What should you do?
- A. Create a records management disposition.
- B. Perform a content search.
- C. Perform an audit search.
- D. Perform a user data search.
Answer: B
NEW QUESTION # 36
You have a Microsoft 365 E5 subscription that uses Microsoft Defender and an Azure subscription that uses Azure Sentinel.
You need to identify all the devices that contain files in emails sent by a known malicious email sender. The query will be based on the match of the SHA256 hash.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.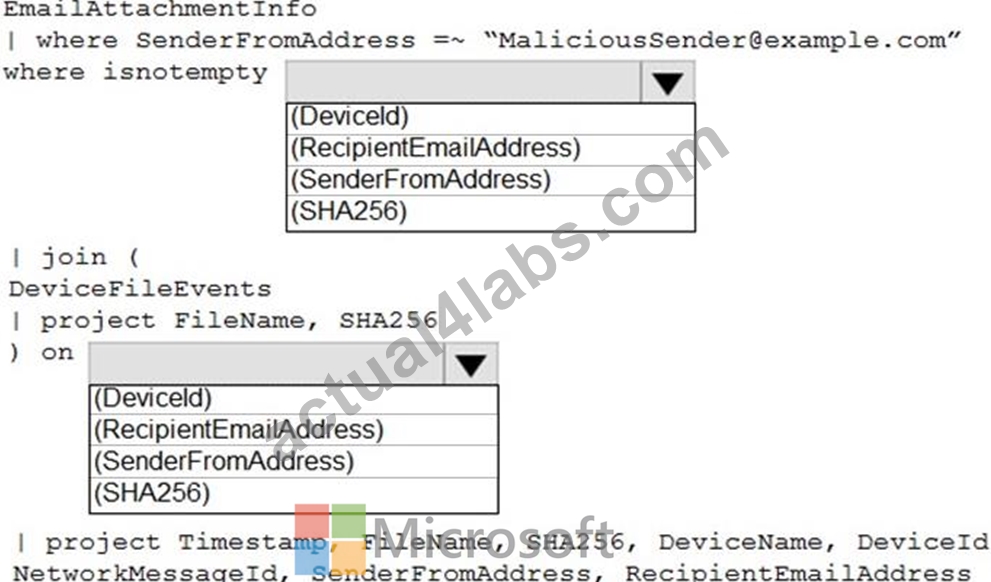
Answer:
Explanation: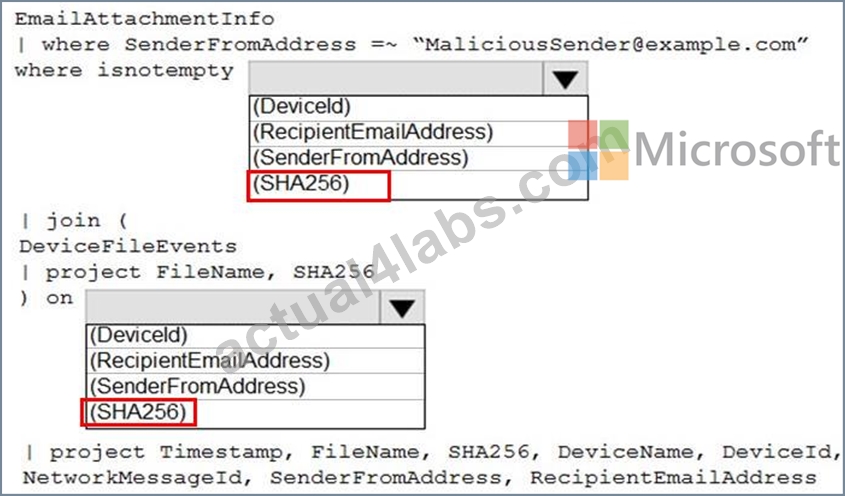
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender/advanced-hunting-query-emails-devices?view=o365-worldwide
NEW QUESTION # 37
You need to configure DC1 to meet the business requirements.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.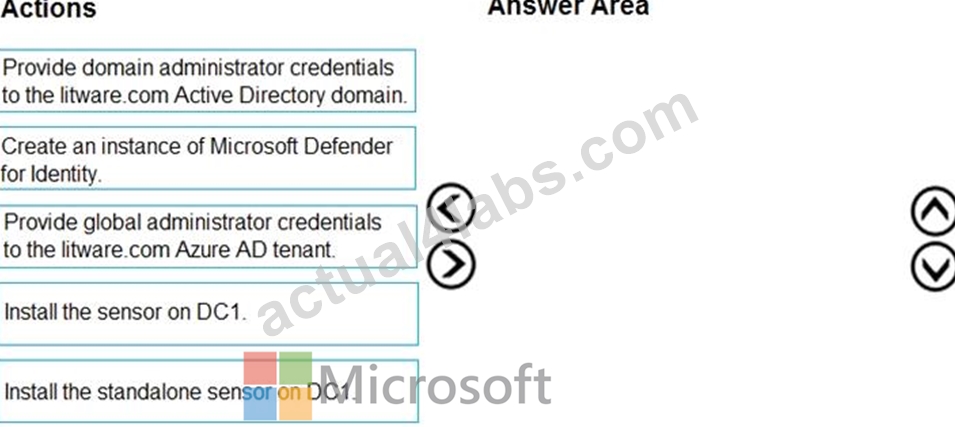
Answer:
Explanation: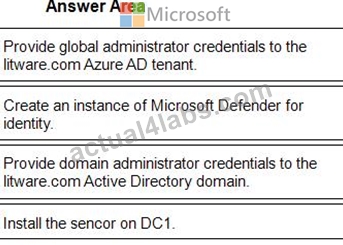
1 - Provide global administrator credentials to the litware.com Azure AD tenant.
2 - Create an instance of Microsoft Defender for identity.
3 - Provide domain administrator credentials to the litware.com Active Directory domain.
4 - Install the sencor on DC1.
Reference:
https://docs.microsoft.com/en-us/defender-for-identity/install-step1
https://docs.microsoft.com/en-us/defender-for-identity/install-step4
Topic 1, Litware inc.
Existing Environment
Identity Environment
The network contains an Active Directory forest named litware.com that syncs to an Azure Active Directory (Azure AD) tenant named litware.com.
Microsoft 365 Environment
Litware has a Microsoft 365 E5 subscription linked to the litware.com Azure AD tenant. Microsoft Defender for Endpoint is deployed to all computers that run Windows 10. All Microsoft Cloud App Security built-in anomaly detection policies are enabled.
Azure Environment
Litware has an Azure subscription linked to the litware.com Azure AD tenant. The subscription contains resources in the East US Azure region as shown in the following table.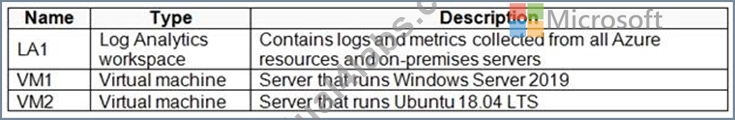
Network Environment
Each Litware office connects directly to the internet and has a site-to-site VPN connection to the virtual networks in the Azure subscription.
On-premises Environment
The on-premises network contains the computers shown in the following table.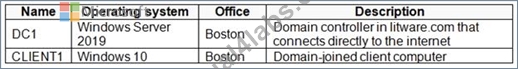
Current problems
Cloud App Security frequently generates false positive alerts when users connect to both offices simultaneously.
Planned Changes
Litware plans to implement the following changes:
Create and configure Azure Sentinel in the Azure subscription.
Validate Azure Sentinel functionality by using Azure AD test user accounts.
Business Requirements
Litware identifies the following business requirements:
Azure Information Protection Requirements
All files that have security labels and are stored on the Windows 10 computers must be available from the Azure Information Protection - Data discovery dashboard.
Microsoft Defender for Endpoint Requirements
All Cloud App Security unsanctioned apps must be blocked on the Windows 10 computers by using Microsoft Defender for Endpoint.
Microsoft Cloud App Security Requirements
Cloud App Security must identify whether a user connection is anomalous based on tenant-level data.
Azure Defender Requirements
All servers must send logs to the same Log Analytics workspace.
Azure Sentinel Requirements
Litware must meet the following Azure Sentinel requirements:
Integrate Azure Sentinel and Cloud App Security.
Ensure that a user named admin1 can configure Azure Sentinel playbooks.
Create an Azure Sentinel analytics rule based on a custom query. The rule must automatically initiate the execution of a playbook.
Add notes to events that represent data access from a specific IP address to provide the ability to reference the IP address when navigating through an investigation graph while hunting.
Create a test rule that generates alerts when inbound access to Microsoft Office 365 by the Azure AD test user accounts is detected. Alerts generated by the rule must be grouped into individual incidents, with one incident per test user account.
NEW QUESTION # 38
You have a Microsoft Sentinel workspace named sws1.
You need to create a hunting query to identify users that list storage keys of multiple Azure Storage accounts. The solution must exclude users that list storage keys for a single storage account.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.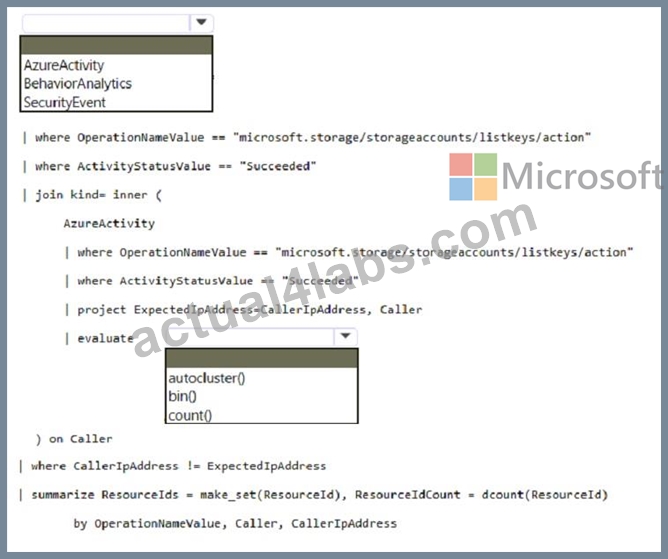
Answer:
Explanation: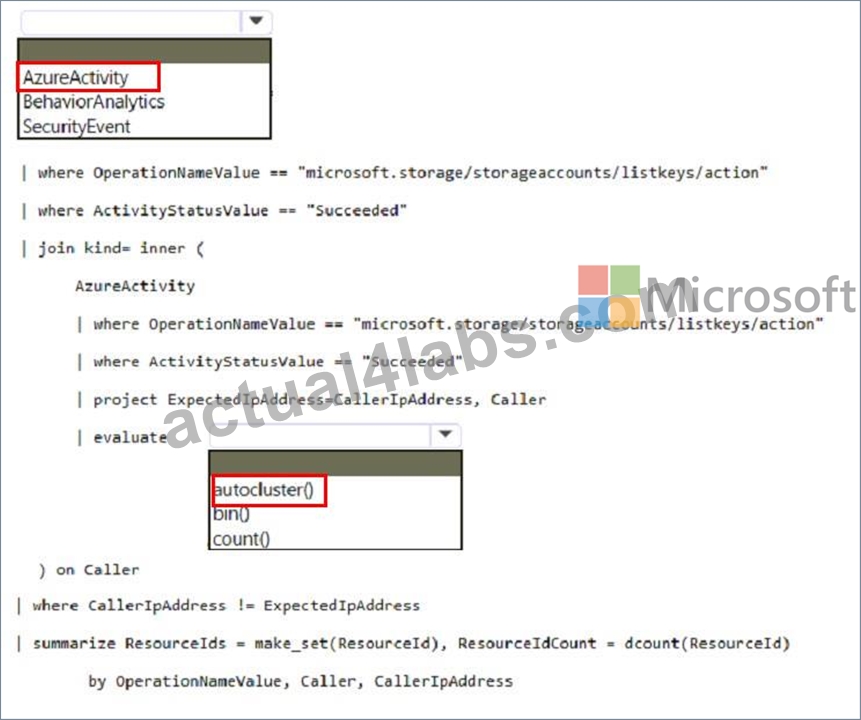
NEW QUESTION # 39
You need to visualize Azure Sentinel data and enrich the data by using third-party data sources to identify indicators of compromise (IoC).
What should you use?
- A. Azure Monitor
- B. Microsoft Cloud App Security
- C. notebooks in Azure Sentinel
- D. hunting queries in Azure Sentinel
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/notebooks
NEW QUESTION # 40
You have an Azure subscription that contains an Microsoft Sentinel workspace.
You need to create a hunting query using Kusto Query Language (KQL) that meets the following requirements:
* Identifies an anomalous number of changes to the rules of a network security group (NSG) made by the same security principal
* Automatically associates the security principal with an Microsoft Sentinel entity How should you complete the query? To answer, select the appropriate options in the answer area. NOTE:
Each correct selection is worth one point.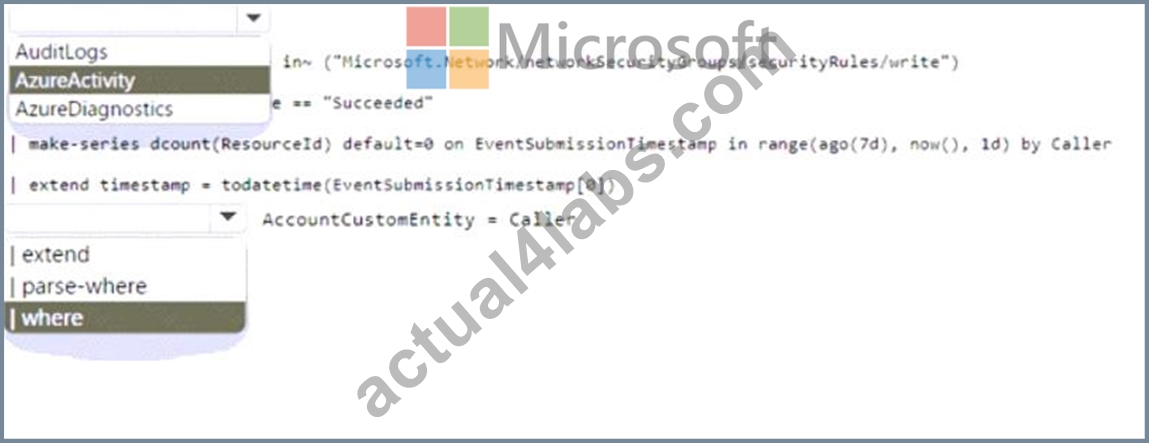
Answer:
Explanation: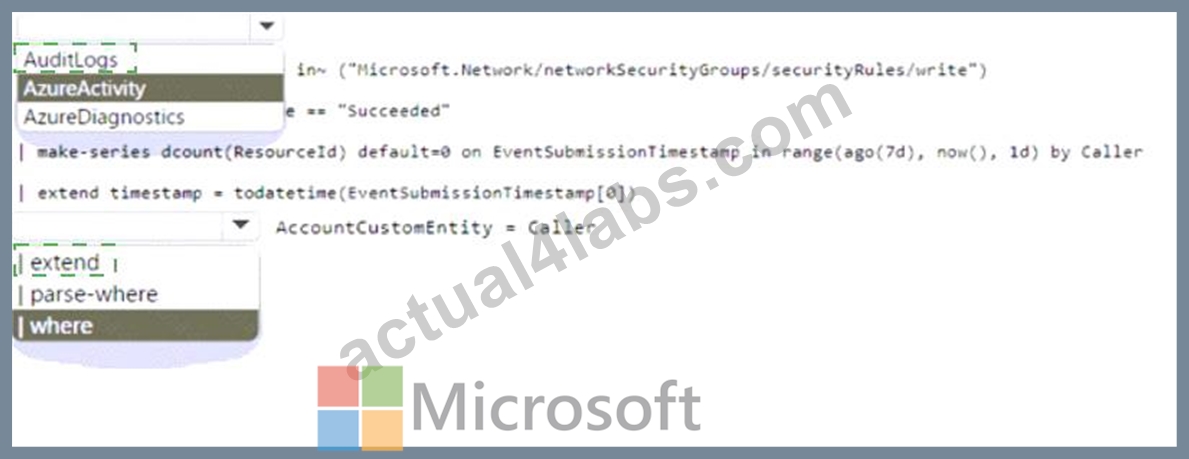
NEW QUESTION # 41
You have four Azure subscriptions. One of the subscriptions contains a Microsoft Sentinel workspace.
You need to deploy Microsoft Sentinel data connectors to collect data from the subscriptions by using Azure Policy. The solution must ensure that the policy will apply to new and existing resources in the subscriptions.
Which type of connectors should you provision, and what should you use to ensure that all the resources are monitored? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.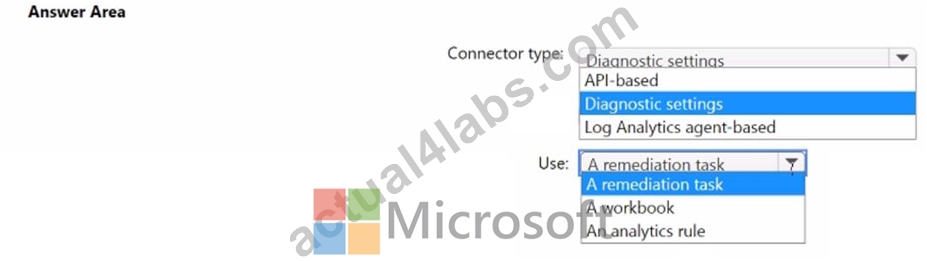
Answer:
Explanation: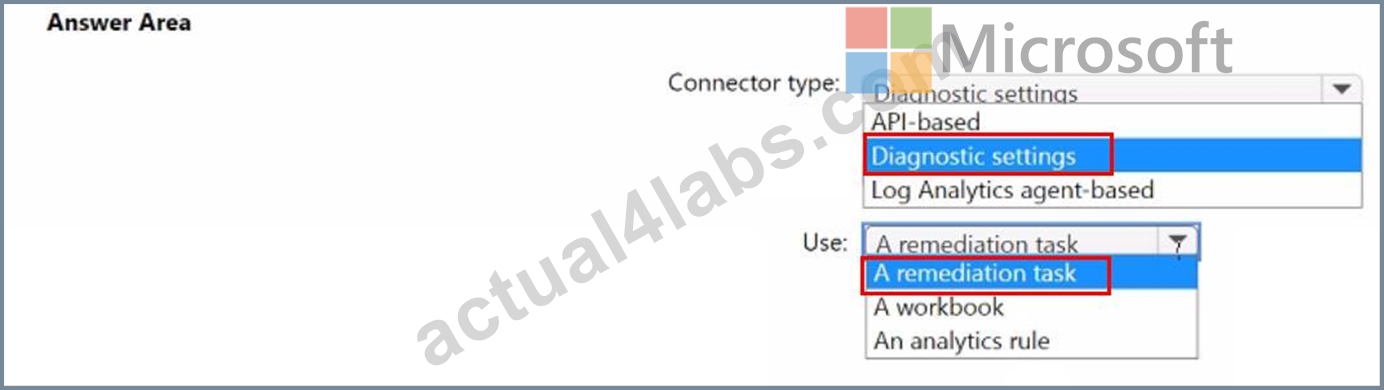
NEW QUESTION # 42
You have a Microsoft Sentinel workspace that contains an Azure AD data connector.
You need to associate a bookmark with an Azure AD-related incident.
What should you do? To answer, drag the appropriate blades to the correct tasks. Each blade may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content NOTE: Each correct selection is worth one point.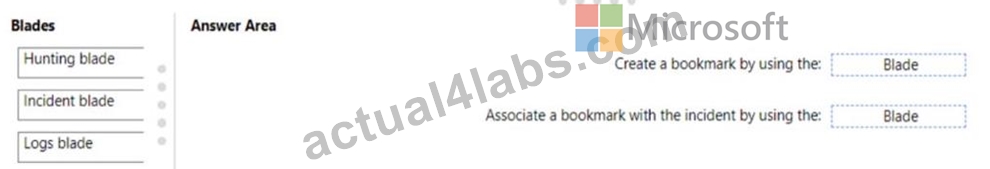
Answer:
Explanation: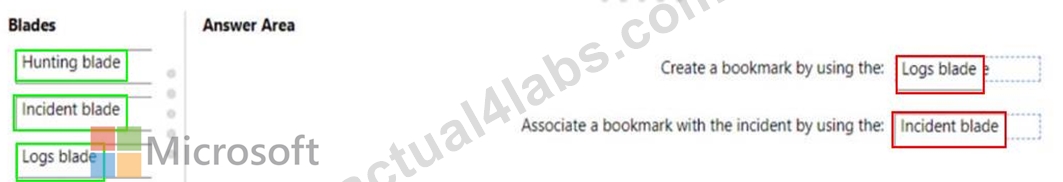
NEW QUESTION # 43
......
SC-200 Exam Dumps - Free Demo & 365 Day Updates: https://www.actual4labs.com/Microsoft/SC-200-actual-exam-dumps.html
Pass SC-200 Exam with Updated SC-200 Exam Dumps PDF: https://drive.google.com/open?id=1W4T_WYn87jNkxKaH_rrB4RUtvjypfwcW